We secure the networks and systems that government departments and healthcare providers in Himachal Pradesh can’t afford to have go down or leak: firewalls, encryption, authentication and monitoring built around what you’re actually protecting, not a generic checklist. We work from Shimla, on systems already live in production — not just in a pitch deck.
What an audit gives you
An audit is a fixed piece of work with a document at the end of it, not a subscription you’re signed up to:
- Scope. We agree what’s in and what isn’t — which systems, which vendors, which processes — before anyone touches anything.
- Collection. Configurations, access controls, vendor practices and documentation reviewed against what’s actually deployed, not what the network diagram says.
- Testing. Security controls tested rather than taken on trust, alongside a look at how the processes around them hold up.
- Report. Findings ranked by what’s genuinely exposed, each with a recommendation specific enough for someone to act on.
We audit systems in IT and technology, finance and banking, healthcare, education, e-commerce and corporate environments. What’s at risk differs in each — a patient record and an order history are not the same problem — so the checklist doesn’t transfer, and we don’t pretend it does.
The network underneath
Security that stops at the application misses where most incidents start. We design and run the network itself:
- Failover and load balancing across multiple ISPs, so one provider going down doesn’t stop the office
- VLAN separation and switch and router configuration, so one compromised device can’t reach everything
- Endpoint protection on the laptops, desktops and phones that are the usual way in
- WiFi planned against a floor plan — access point placement, interference management, guest traffic kept off the staff network
- Structured cabling, labelled and documented, including runs for CCTV, IP phones, printers and IoT devices
We’ve built and maintained these in offices, hotels, retail outlets, schools, clinics and industrial sites. Each one fails differently, which is why the design starts with the building and the traffic rather than a hardware list.
What's included
How we scope this
Firewall & network hardening
A monitored barrier between your internal network and the internet, tuned to your actual traffic, not a default ruleset.
Malware and intrusion detection
Continuous scanning that catches threats before they reach production, not after an incident report.
Data encryption & secure authentication
Multi-factor authentication and encryption in transit and at rest, so a stolen credential isn't a stolen database.
24/7 monitoring and response
A team watching for the alert, not a dashboard nobody checks until Monday.
Third-party security audits
Independent evaluation of systems, vendors and processes against compliance standards, for IT, finance, healthcare, education, e-commerce and corporate clients.
Network design and connectivity
Multi-ISP failover, VLAN separation, structured cabling and WiFi planned against a floor plan — the layer where most incidents actually start, designed rather than accumulated.
How we work
The process, in order
- 01
Audit
We review the current network, systems and access controls against what's actually at risk, not a generic checklist.
- 02
Harden
Firewalls, encryption and authentication configured around what the audit found, not a default ruleset applied everywhere.
- 03
Monitor
24/7 scanning and alerting once the hardened setup is live, so an anomaly gets caught before it's an incident.
- 04
Respond
A defined incident process with an owner and a next step, not just an entry in a log nobody reads.
Shipped work
What this looks like in production
Public-sector portals we built and continue to run. Hardening and monitoring aren't a separate engagement on these — they're the reason they've stayed up.
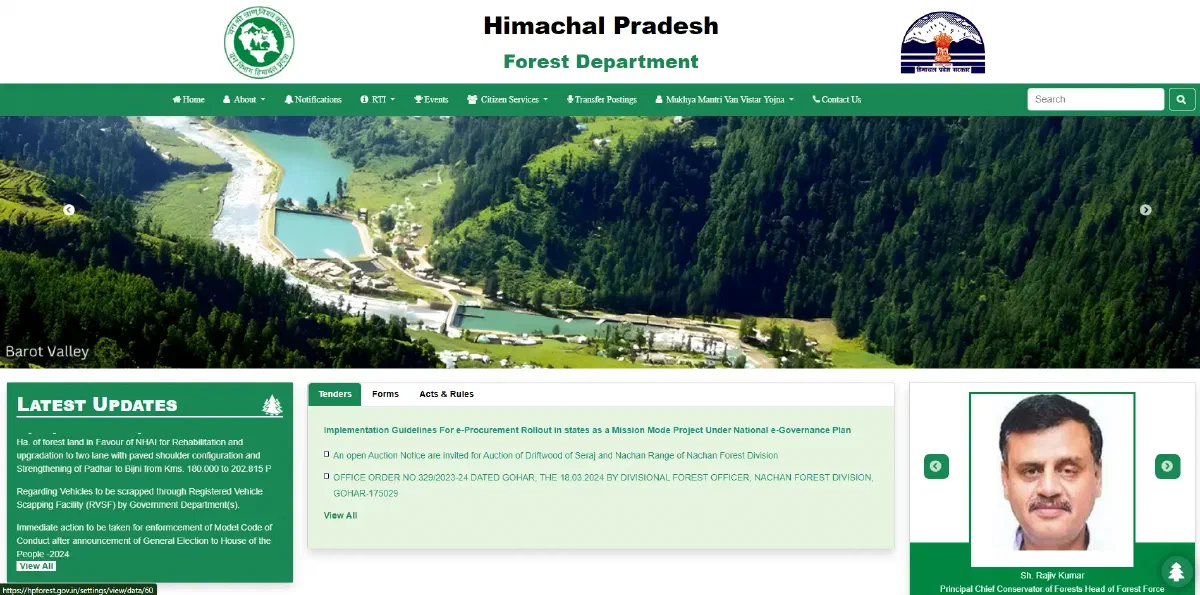
Government & public sector
Himachal Pradesh Forest Department
Departmental portal running tenders, forms, acts and rules, RTI, transfer postings and citizen services behind a single search.
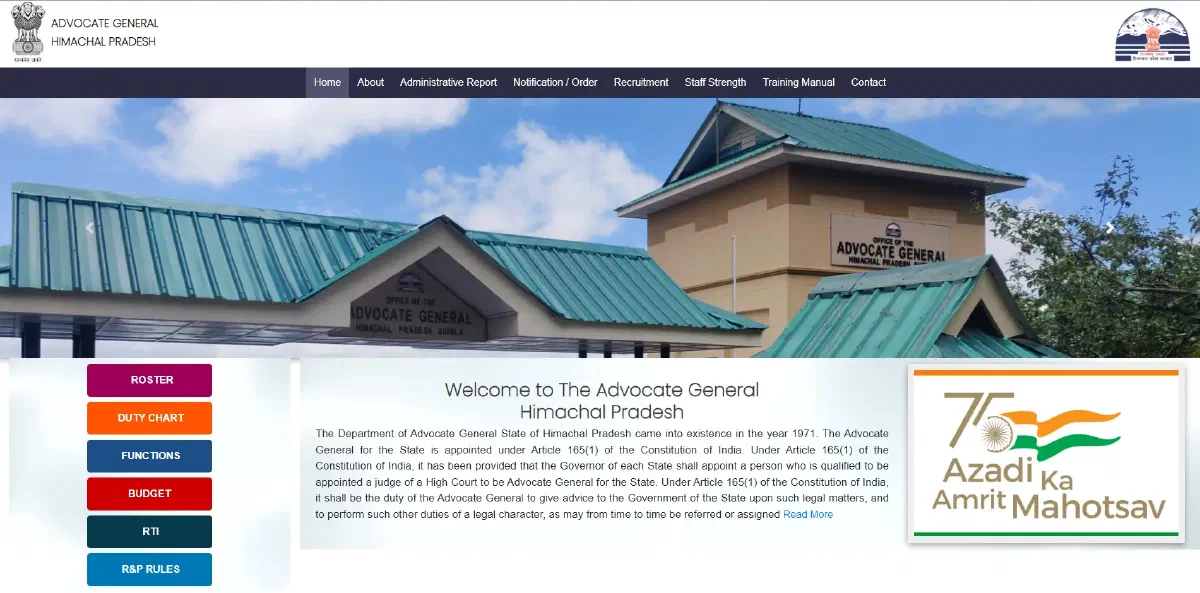
Government & public sector
Advocate General, Himachal Pradesh
Law office portal publishing the roster, duty chart, administrative reports, notifications and recruitment under an RTI-compliant structure.
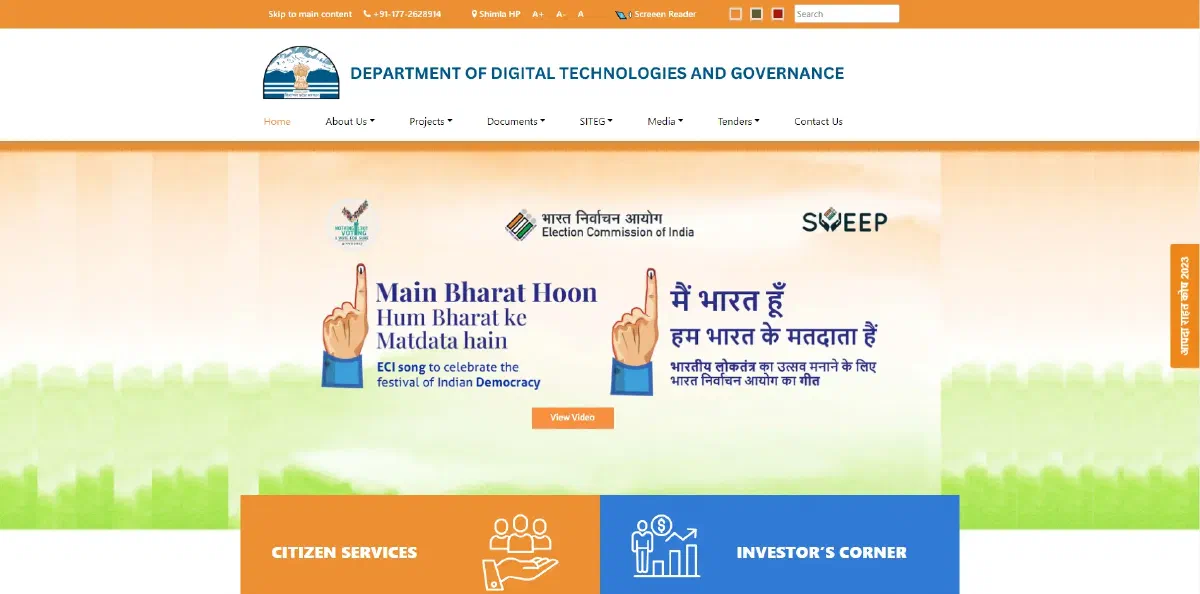
Government & public sector
Department of Digital Technologies and Governance
State e-governance portal with a projects and documents library, tender listings, and split citizen-services and investor entry points.
FAQ